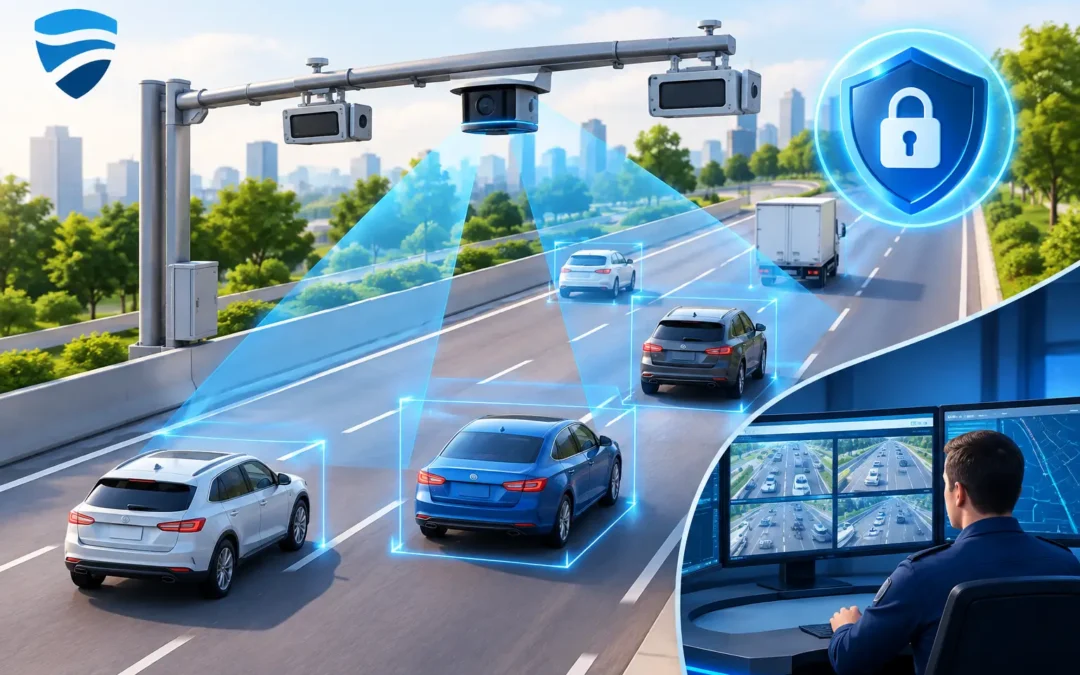
A roadside detector can influence signal timings, priority calls, speed displays and operational decisions within seconds. That makes the best traffic sensor security controls a practical requirement, not an IT afterthought. If a sensor is incorrectly configured, physically damaged or connected through an inadequately protected network, detection quality and junction performance can suffer long before the issue is recognised.
For highways authorities, contractors and signal engineers, the objective is straightforward: preserve trustworthy detection from the roadside device through to the controller, platform and operator. The right controls should protect availability as well as data. A perfectly encrypted sensor feed is of little value if a damaged cabinet, failed power supply or unavailable communications link leaves a junction operating without its required detection.
Security starts with the sensor architecture
Security requirements should be set during scheme design, alongside detection zones, mounting positions, communications and power arrangements. Retrofitting controls after commissioning can introduce avoidable site visits, configuration changes and uncertainty over accountability.
Above-ground radar, AI video and wireless detection technologies provide a useful advantage over road-embedded loops: they can usually be installed, inspected and replaced without carriageway excavation. This reduces disruption and removes one common point of failure beneath the road surface. It does not, however, remove the need to secure the detector itself, its enclosure, its cabling and the data path it uses.
A sensible design begins by identifying what the sensor can affect. A vehicle detector providing a non-critical monitoring count has a different risk profile from one that calls a stage at a signalised junction, supports bus priority or informs a safety-related warning system. The more direct the operational consequence, the tighter the control of access, configuration and fault response should be.
Best traffic sensor security controls by layer
Effective control is layered. No single password, lock or network setting will protect a traffic detection deployment on its own. The following areas should be specified together.
Physical protection at the roadside
Detection devices should be installed at a height and location that supports their performance while limiting casual interference. Pole-mounted equipment needs tamper-resistant fixings, protected cable entry points and weatherproof enclosures suitable for the location. Cabinets and feeder pillars require controlled access, with keys, access records and contractor permissions managed properly.
Physical security also includes the less obvious details. Exposed Ethernet leads, unprotected power converters and poorly sealed gland plates can create both reliability and security weaknesses. At locations with a known history of vandalism, consider more resilient mounting arrangements, cabinet alarms or remote indication of door openings. These measures should be proportionate to the site rather than applied indiscriminately.
Secure device configuration
Every detector should have a documented baseline configuration before it enters service. This includes firmware version, detection zones, device address, communications method, authentication settings and the person or organisation responsible for support.
Default usernames and passwords must be changed before commissioning. Unique credentials should be used for each device or site where the system permits it, rather than sharing a single installer password across an estate. Access rights should follow roles: an engineer who needs to review detection health does not necessarily need permission to alter controller-facing settings or create new administrator accounts.
Remote management can reduce attendance costs and speed up fault diagnosis, but it should be enabled only where there is a clear operational need. Disable unused services and ports, restrict management access to authorised networks, and remove temporary commissioning accounts once handover is complete. Configuration backups should be stored securely and version-controlled so that a known-good setup can be restored after a fault or unauthorised change.
Protected communications and network separation
Traffic sensors increasingly exchange data with signal controllers, edge processors and central analytics platforms. That connectivity creates operational value, but it also means the detector must not be treated as an isolated roadside asset.
Separate detection devices from general corporate IT networks wherever practical. Network segmentation limits the impact of a compromised endpoint and makes monitoring more meaningful. Use authenticated, encrypted communications where supported, particularly for data crossing public, cellular or shared networks. For wireless sensors, protect the radio network with current encryption, controlled device enrolment and a process for revoking a lost or replaced unit.
It is equally important to control connections between the detection network and signal systems. Only the required protocols and ports should be allowed. A device used for traffic counting or classifier data should not have unrestricted reach into controller or operational technology environments. This principle of least privilege helps contain faults and reduces the opportunity for lateral movement between systems.
Firmware, patching and supply-chain assurance
A sensor remains a managed asset throughout its service life. Manufacturers may issue firmware updates to correct faults, improve detection performance or address newly identified vulnerabilities. Authorities should maintain an asset register that records installed model, serial number, firmware level, location and support status. Without this information, it is difficult to establish which sites require action when an advisory is issued.
Updates need testing before broad deployment. A firmware change that is secure but alters detection behaviour, communications timing or compatibility with an existing controller can create an operational problem. Test representative devices in a controlled environment where possible, agree a rollback plan and schedule live updates for periods that minimise network risk.
Procurement should also examine supplier practices. Ask how vulnerabilities are reported and handled, how long security updates are supported, whether software integrity is checked, and what access a supplier requires for remote diagnostics. Product capability matters, but a clear lifecycle support process often determines whether a control remains effective several years after installation.
Monitoring, logging and anomaly response
Security events and operational faults can look similar at first. A detector dropping offline may be caused by a power issue, damaged cable, communications outage, software fault or unauthorised interference. Monitoring should provide enough information for teams to distinguish between these possibilities quickly.
Record configuration changes, remote logins, device restarts, loss of communications and unusual detection states. Alerts should be prioritised to avoid overwhelming the duty team with routine messages. For example, an intermittent data gap from a non-critical counter may be handled through maintenance planning, while loss of detection at a heavily used signal junction may require immediate review.
A short, rehearsed response process is more valuable than an extensive document that no one uses. It should identify who validates the fault, who can isolate a device, who contacts the supplier, how the junction is kept safe during degraded operation, and how evidence is retained. For managed networks, this should align with existing incident management and traffic control procedures.
Match the controls to the application
Not every scheme needs the same level of protection. A temporary traffic survey sensor, for example, may rely on a limited wireless deployment and local data collection. Its controls should focus on secure commissioning, device accountability, physical removal at the end of the survey and protection of any collected data.
A permanent AI video detector at a busy urban junction requires a broader approach. It may process imagery at the edge, provide vehicle, cyclist and pedestrian presence, and pass calls into a signal system. Here, secure access, privacy-conscious configuration, protected backhaul, audit logging and defined maintenance responsibilities become central to performance.
Radar detection can reduce some privacy considerations because it does not rely on identifiable imagery in the same way as video. Yet it still needs protection against configuration changes, communications loss and physical interference. Technology choice changes the control emphasis; it does not eliminate the need for security engineering.
Build security into acceptance testing
Commissioning is the point at which specifications become evidence. Acceptance testing should confirm more than detection accuracy and zone coverage. It should verify that default credentials have been removed, unauthorised access is rejected, approved users have the correct permissions, remote management routes are restricted, and event logs are available to the responsible team.
Test what happens when communications fail. Does the detector recover correctly? Does the controller enter its intended fallback mode? Is an alert raised, and does it reach the right person? These are operational questions, but they are inseparable from security because availability is a core security outcome for traffic infrastructure.
C & T Technology approaches above-ground detection as part of the wider traffic management system, not as a standalone roadside product. That perspective helps ensure radar, video and wireless sensors are selected and configured around the actual junction, corridor or network objective.
The most effective control is a clear ownership model: know every device, know what it is permitted to do, know who can change it, and know how the site should behave when it cannot be trusted. With that discipline in place, smarter detection can support safer roads and more reliable network operation without creating an unmanaged point of risk.